01
Stay curious, keep learning
Growth comes from asking questions, seeking context, and pushing beyond comfort zones.
About Clearly AI
Emily and Joe Choi-Greene founded Clearly AI in Seattle in 2024, after running hundreds of security reviews at Amazon. We've raised $8.4M from Basis Set Ventures, Crosspoint Capital Partners, and more, and we were named a Top 10 Finalist in the RSAC 2026 Innovation Sandbox.
Trusted by product security, privacy, and GRC teams across automotive, telecom, fintech, and more
Emily and Joe met in 2019 on the same Alexa security review at Amazon. Hundreds of reviews later, they got married and started a company to fix the process they'd both been stuck in.
Emily Choi-Greene and Joe Choi-Greene, co-founders of Clearly AI.
Co-Founder & CEO
Led Alexa AI Security at Amazon, then owned data security and privacy at Moveworks (acquired by ServiceNow). Hundreds of security and privacy reviews, from AI data lifecycles to an ML compute platform used by 5,000+ scientists. Computer Science, High Honors, Dartmouth.
Co-Founder & CTO
Senior software engineer at Amazon. Led satellite telemetry for Project Kuiper, built exabyte-scale data lakes at Alexa, and automated data compliance for regulations like GDPR and HIPAA. Computer Science, Carnegie Mellon.
Watch the pitch
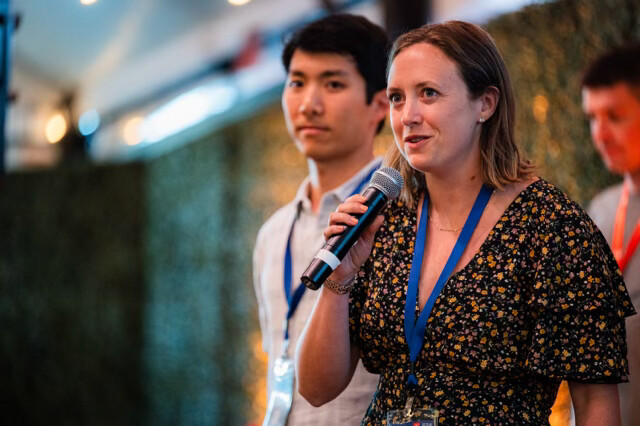
In March 2026, Emily pitched Clearly AI on the main stage at the RSAC Innovation Sandbox as one of 10 finalists selected from hundreds of submissions. The whole problem, and how we solve it, in three minutes.
Emily Choi-Greene, CEO of Clearly AI, at the RSAC 2026 Innovation Sandbox.
Why we built this
Engineering teams ship faster than ever, and AI-written code is widening the gap. Security teams are still responsible for everything, and most formally review 10–15% of it. The rest ships without a documented assessment: not by choice, but because every review starts from a blank whiteboard. So we built the platform we wished we had.
The typical approach
A fraction of launches get reviewed. The rest can get deferred until after launch.
Clearly AI
Every change that ships gets a threat model, triggered from Jira, GitHub, and more
How continuous threat modeling worksThe typical approach
Meetings, whiteboards, and diagrams before a single finding
Clearly AI
Point it at a ticket, design doc, or repo. Agents gather the context and draft the assessment.
See security intakeThe typical approach
Findings vary by reviewer. Hard to defend in an audit.
Clearly AI
Every finding cites its source. Versioned templates make results consistent and auditable.
The typical approach
One tool for threat models, another for vendors, spreadsheets for the rest
Clearly AI
Threat models, PIAs, vendor risk, AI risk, and compliance reviews on one platform and one license
Explore the platformThe typical approach
Findings live in a doc nobody reopens
90%
Reduction in review turnaround time
4x
Review capacity with the same headcount.
From 10 to
100%
Product coverage
“Security doesn't break down because of bad tools or bad engineers. It breaks down when the right information doesn't reach the right people at the right time.”
What we believe
We are rebuilding how regulated enterprises decide what's safe to ship. These are the principles behind every release.
Developers skip security when it's slow. Take the friction out, and doing it right becomes the default.
Security engineers know security. Developers know their systems. Most risk sits in the gap between them, so that's where Clearly AI works.
We label what's live, what's in beta, and what's coming soon. If it's on the roadmap, we'll call it a roadmap item and show you where it stands.
Gathering context and drafting findings should be automated. Weighing tradeoffs, reasoning about attack paths, and signing off should stay human.
Join us
People join Clearly AI to use AI to improve security across the industries everyone depends on: financial services, energy, telecom, automotive, and more.
Security engineering in 2035 will look nothing like it does today. It'll be more interesting, a lot more fun, and closer to wizardry, or running a legion of agents. The people here get to define what that looks like.
Our team is made up of the best security nerds in the business, who've tackled security at scale at companies like Amazon, Google, Airbnb, Twilio, Lyft, NetSPI, Microsoft, Meta, Apple, Palo Alto Networks, GitLab, and more.
01
Growth comes from asking questions, seeking context, and pushing beyond comfort zones.
02
Creativity and resourcefulness beat polish and over-planning. Action matters more than perfection.
03
Grit, energy, and intentionality fuel progress. We move with clarity, not just momentum.
04
No noise, no jargon. Share context, listen first, and make sure everyone understands.
05
Have strong beliefs, but hold them lightly. Confidence paired with openness earns trust.
06
Understand teammates and customers deeply. Compassion drives better products and stronger teams.
07
We win as a team. Share context, align, and build together.
08
Respect is non-negotiable. Talent never excuses arrogance or intolerance.
09
Keep it simple, keep it fast. Process should enable, not block progress.
10
Integrity over shortcuts. We earn trust by doing what's right for customers, teammates, and the company.
11
AI should augment humans and make our lives better. Work should support life, not consume it.
12
Privacy and security are foundational. We lead by example, protect data relentlessly, and practice the same standards we expect others to uphold.
$8.4M seed from Basis Set Ventures, Crosspoint Capital Partners, Argon Ventures, Ritual Capital, and Y Combinator, plus angels who've run security and privacy programs at companies like Amplitude, OKX, Brex, and Meta.
fmr CEO, Reddit
CISO, Kodiak Robotics
fmr CISO, Amplitude
Head of Privacy & DPO, Brex
fmr CISO, OKX
Staff Privacy Engineer, Meta
Director of Identity & Security, Charter Communications
VP, Google Assistant
Sr Principal Cybersecurity Architect, JP Morgan Chase
Chief Strategy Office, Air
Former CISO Chevron and Costco
Security and trust
You'll hand us design docs, code, and vendor data. The criticality of this isn’t lost on us. Clearly AI is SOC 2 Type II audited, never trains on your data, and deploys the way your security team requires: multi-tenant, single-tenant, or in your own cloud. We even run our own vendor reviews and threat models on Clearly AI.
FAQ
Emily Choi-Greene (CEO) and Joe Choi-Greene (CTO) founded Clearly AI in 2024. Both are engineers who ran hundreds of security and privacy reviews at Amazon and Moveworks.
Seattle, Washington and remotely across the US. We work with enterprise customers across the US and Europe.
Clearly AI has raised $8.4M in seed funding from Basis Set Ventures, Crosspoint Capital Partners, Argon Ventures, Ritual Capital, and Y Combinator, plus angels including former CISOs of Amplitude and OKX.
Yes. Clearly AI has completed a SOC 2 Type II audit, and customers can request the report under NDA.
No. Clearly AI uses retrieval to work from your sources without training on them, and you can bring your own model keys, including Amazon Bedrock.
No. Continuous threat modeling means every change that ships gets a threat model, triggered automatically or on a schedule. Each review is a point-in-time assessment of a specific project version.
Yes! We're growing quickly and are looking for the best of the best.