Clearly AI named Finalist in the RSAC Innovation Sandbox 2026, closing an $8.4 million Seed Round. Read more
Clearly AI

Secure everything that ships

Clearly AI is a continuous threat modeling platform that automates the security review work that outpaces what your team can cover manually, so you can stop firefighting and actually get ahead of what ships.

Trusted by the companies you trust the most

  • HID
  • Ericsson
  • PayPal
  • Modern Health
  • Hagerty
  • Rivian
  • Infineon
  • Bastion

Agentic context

Threat models from what you already have

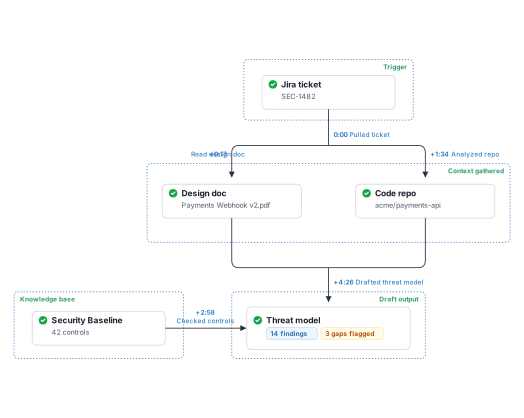
Traditional threat modeling tools start with a blank whiteboard. First comes the kickoff meeting, then the architecture diagram, then the threat category setup, and days pass before a single finding appears. Clearly AI works the other way. Point it at a Jira ticket, a design doc, a GitHub repo, or a vendor questionnaire, and it gathers the context and builds a picture of the system on its own. It then delivers an accurate, structured assessment with findings pre-populated, sources cited, and gaps flagged. This isn't a faster version of the manual process. It doesn't replace your security engineers; it gives them a massive head start. Every conversation with your team and your developers starts from a sourced draft, not a blank page.

How context gathering works

TriggerJira ticketSEC-14820:00 Pulled ticket+0:17 Read design doc+1:34 Analyzed repoContext gatheredDesign docPayments Webhook v2.pdfCode repoacme/payments-api+4:26 Drafted threat modelDraft outputThreat model14 findings3 gaps flaggedKnowledge baseSecurity Baseline42 controls+2:58Checked controls

One platform. From intake to remediation.

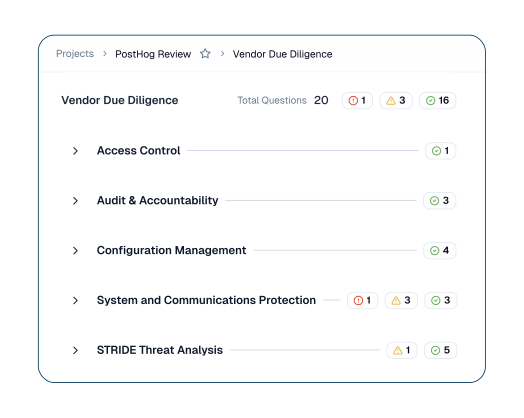
Threat models, privacy impact assessments, vendor risk reviews, and AI governance evaluations all run on the same agents, the same policies, and the same audit trail.

  1. 01 Triage

    Determine whether an employee question, new code change, or new feature ticket needs security’s eyes. Give employees answers quickly and auto-resolve low-risk changes.

  2. 02 Intake

    Ingest the information provided by the business and feed it into the right structured intake for your team. The enterprise context graph links the design docs, repos, tickets, and policies behind every system under review, so no one rebuilds the architecture from scratch.

  3. 03 Review

    Structured assessments, drafted by agents. Findings arrive pre-populated, with sources cited and gaps flagged. Engineers can review through configurable workflows, or bring Clearly AI into the IDE and AI coding tools over MCP.

  4. 04 Resolve

    Track every finding to a verified close. High-criticality findings open Jira tickets or post to Slack automatically. Clearly AI verifies that controls and remediations actually landed, then reports coverage to leadership and auditors.

Audit-ready accuracy

Findings your team can actually stand behind

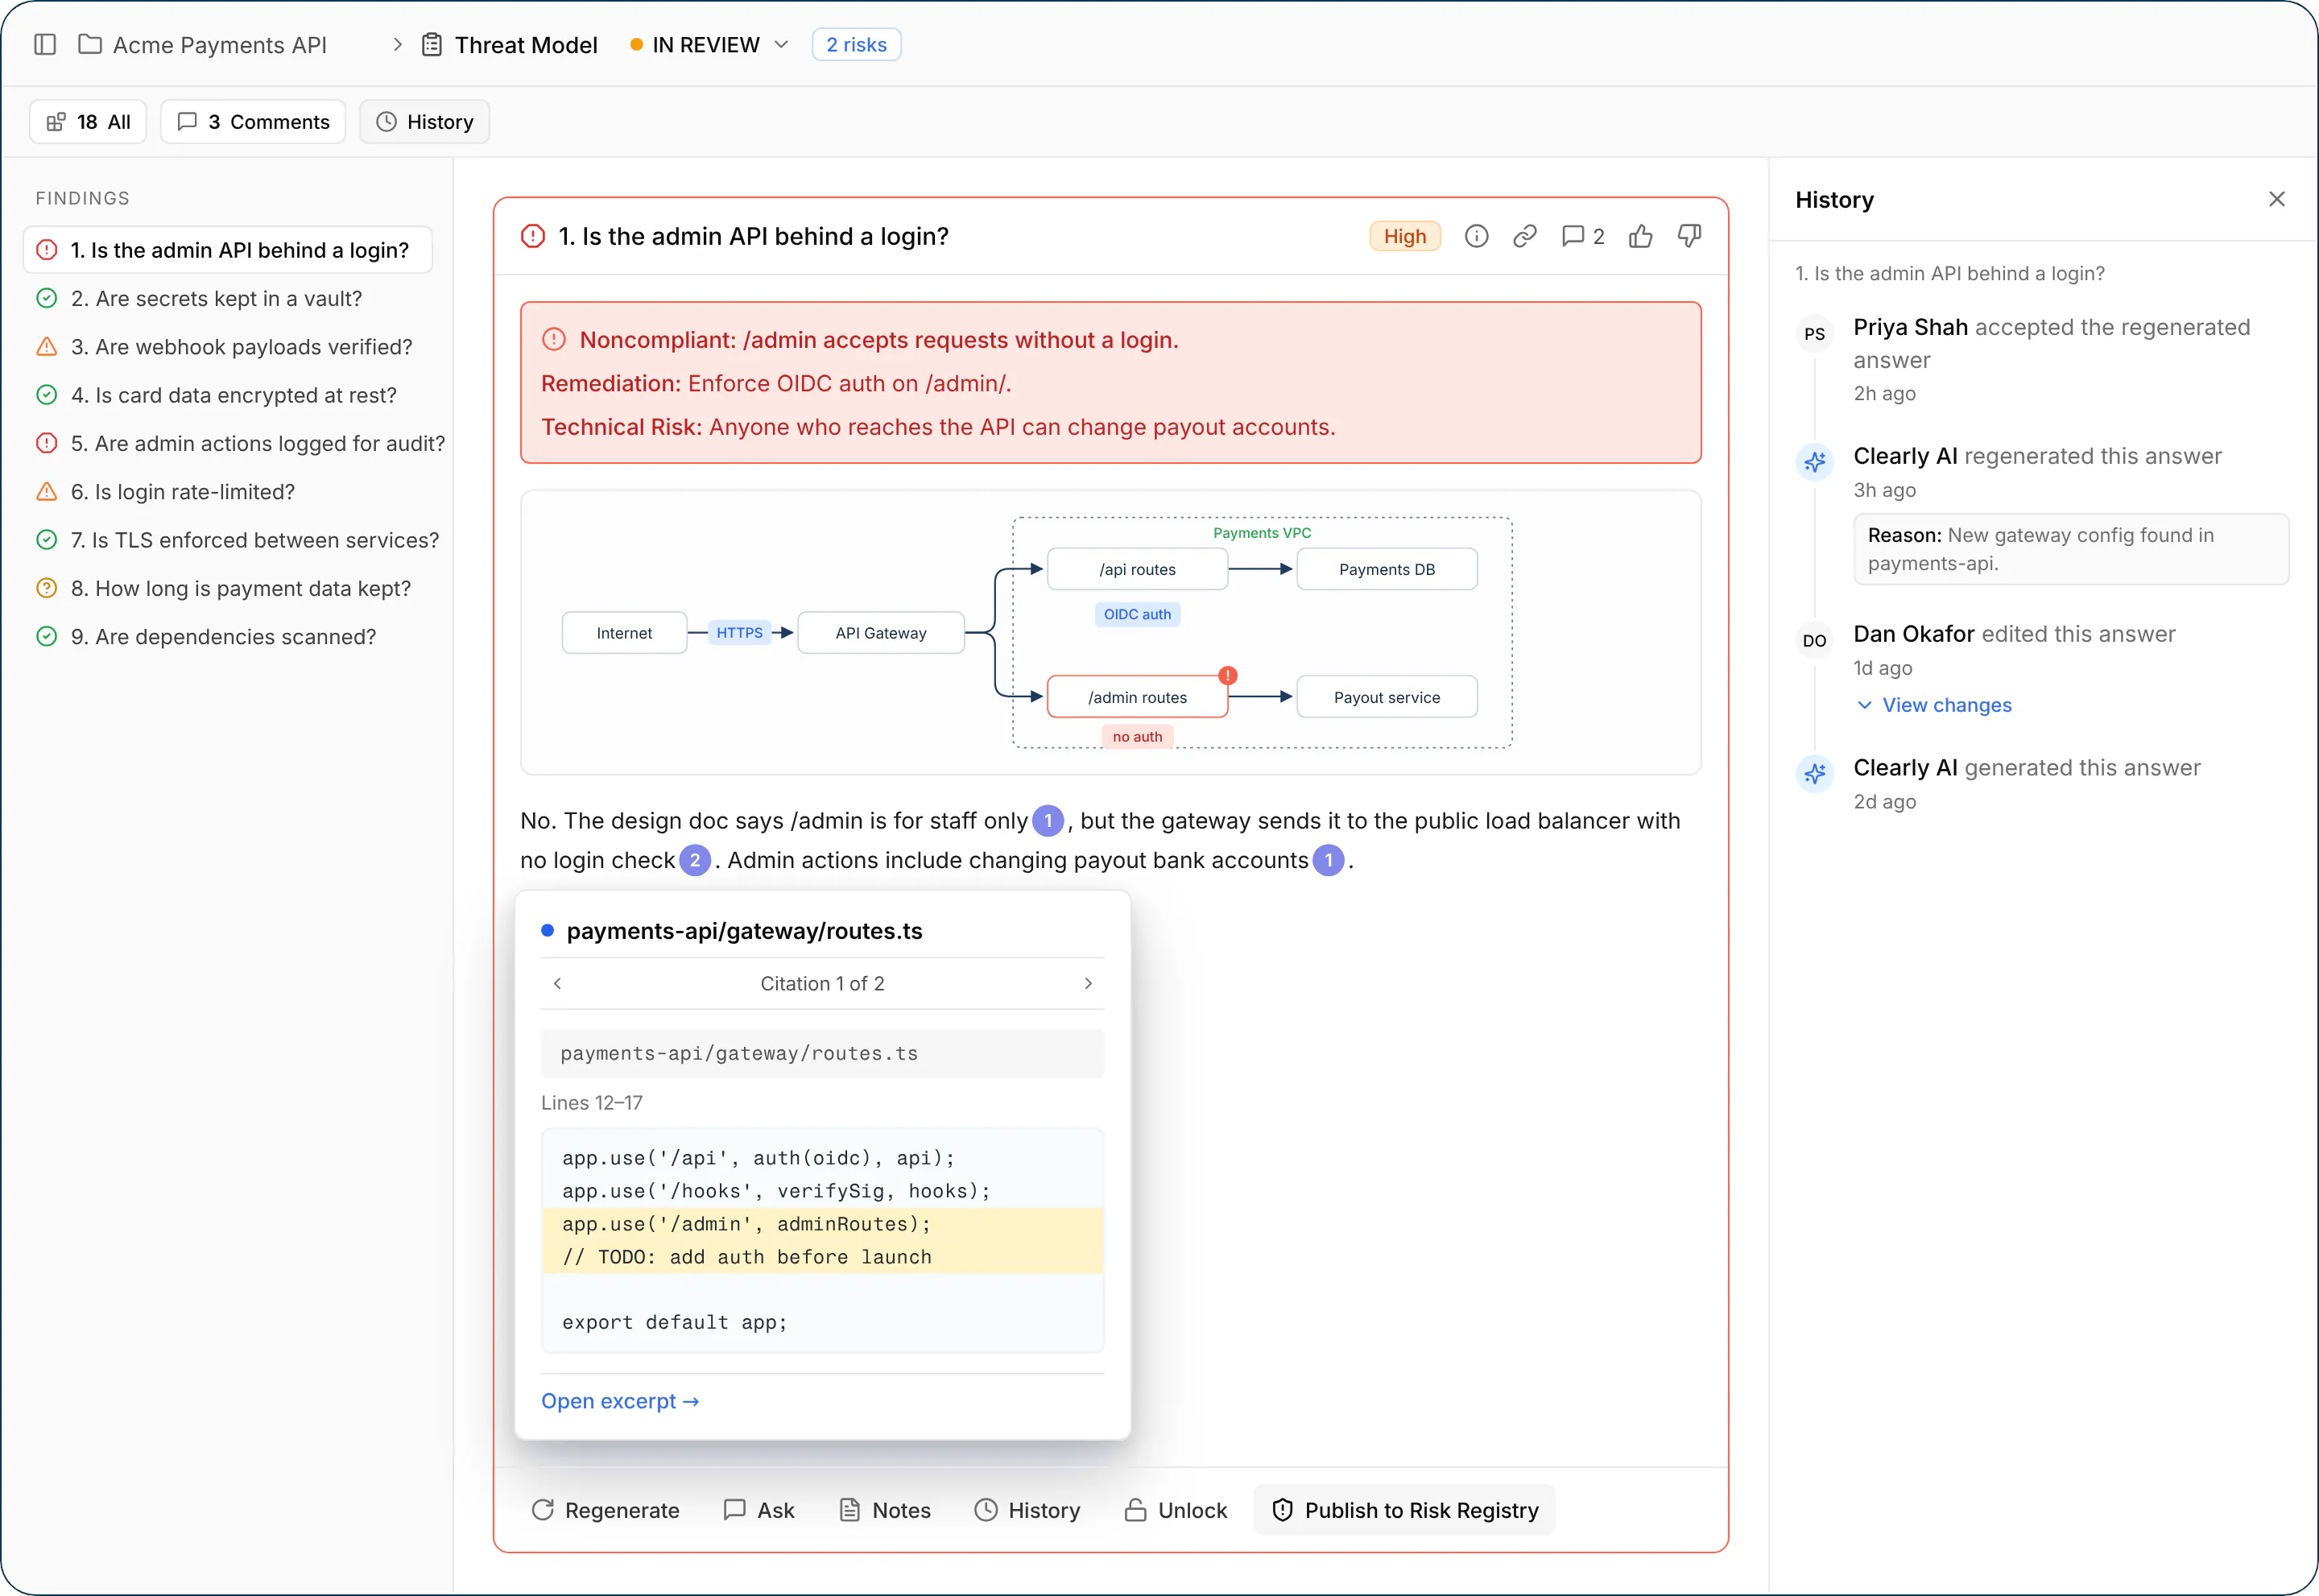
Every finding carries its source: the document, ticket, or code that supports it. Your reviewers can challenge it, push back, and sign it. Review templates are versioned, so results stay consistent and auditable against a specific project state. That's what makes the output defensible in an audit or a regulator conversation.

How tuning & accuracy work

A Clearly AI threat model finding opened from the findings list, with its cited source, reasoning, review history and the Publish to Risk Registry action.

Centralize security and privacy

One platform. Every review your team runs

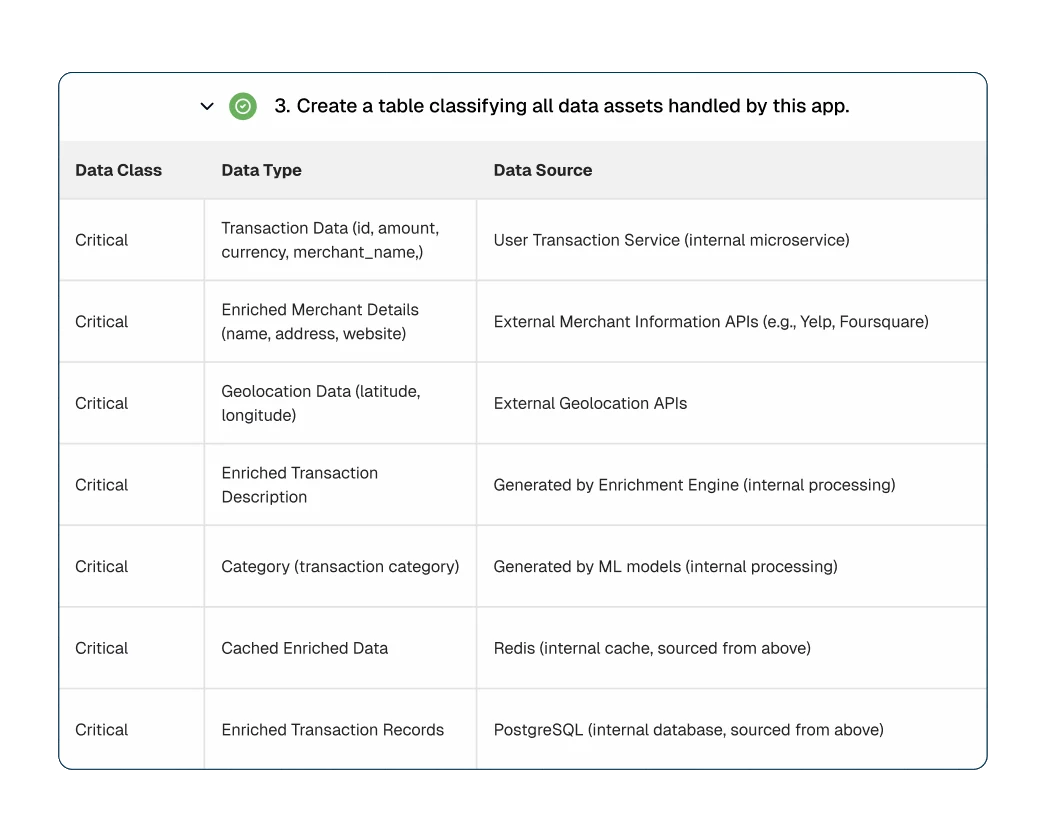
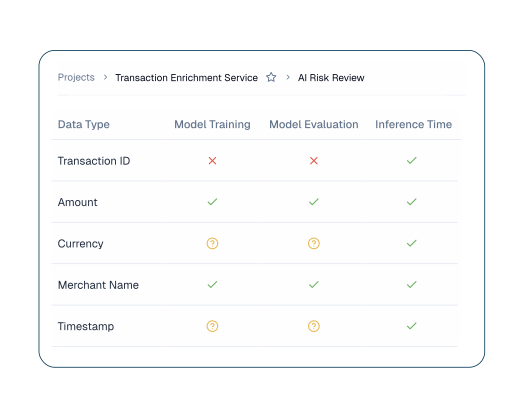
Security teams do more than just threat modeling. They review vendors, assess data flows, evaluate AI systems, and map controls against compliance frameworks. Most tools cover one of those things well and leave the rest to a separate process, a separate configuration, and a separate license.

Clearly AI covers the full scope: threat models, privacy impact assessments, vendor risk assessments, AI risk reviews, and compliance control evaluations, all in one platform running against your policies and frameworks.

When you use Clearly AI for threat modeling, your privacy team and GRC function benefit, too. One investment extends across functions that were previously siloed.

What Clearly AI can do

Product Security

Automate threat modeling and design reviews. Ship secure features faster.

“With Clearly AI, we provided the documentation for the product and within a minute, here's all that documentation generated that would've taken developers weeks to create. We're seeing immediate impact with the threat modeling...weeks reduced down to minutes, literally.”
William Brown, Sr. Director of Product Security and Privacy, HID Global
See product security features
Agent activity for Acme Payments API: pulled ticket SEC-1482, read the design doc, analyzed repo acme/payments-api, checked 42 controls, drafted a threat model with 14 findings and 3 gaps flagged.

Security expertise

The judgment of your best security engineer

Clearly AI was founded by security engineers who ran hundreds of critical reviews at Amazon, and it has a security expert's domain depth, not generic AI retrained for security. It applies the judgment a senior engineer would: what's a real finding versus noise, what context is missing, and what the next step should be. The same rigor applies whether the methodology is STRIDE, ATT&CK, MAESTRO, OWASP, or your own.

How Clearly AI does continuous threat modeling

Internal serviceConfig serviceDatabaseUserAPI gatewayLoad balancerCompute instanceLambda functionStorage bucket

Workflow-native

Runs inside your workflow

Reviews trigger automatically from Jira, GitHub, ServiceNow, Azure DevOps, and Linear, or run on a schedule, with no manual start required. Developers and their AI coding agents can reach Clearly AI in the IDE and over MCP. High-criticality findings create Jira tickets or post to Slack automatically, so findings route back to the tools where security and the business already work.

See all integrations

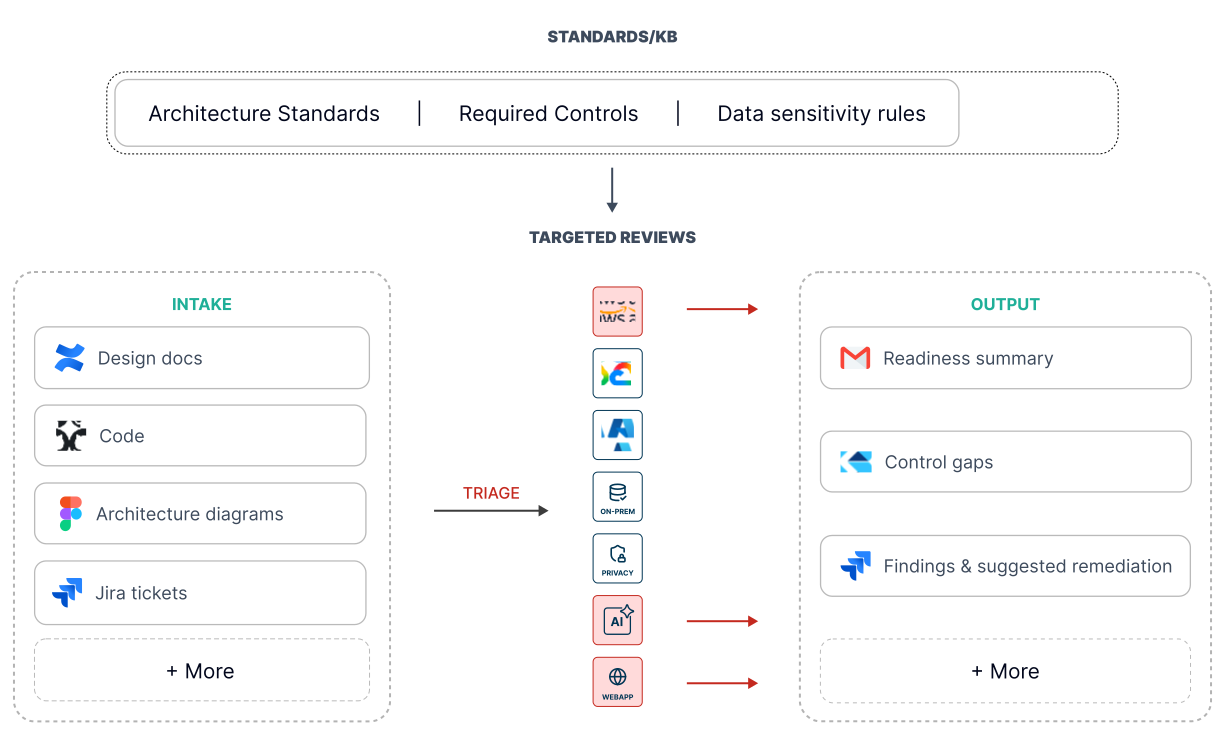
Workflow diagram: intake sources such as design docs, code, architecture diagrams and Jira tickets are triaged against your architecture standards, required controls and data sensitivity rules into targeted reviews, which produce a readiness summary, control gaps, and findings with suggested remediation.

Proven outcomes

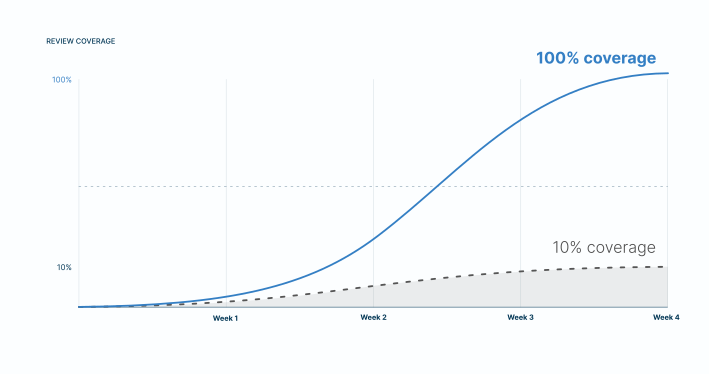
From 10% coverage to 100%

Customers see a ~90% reduction in time per review and 4x review capacity with the same team. That holds across threat modeling, privacy, and vendor risk workflows, not just one assessment type. When coverage expands that way, it's because the output is reliable enough to stake a decision on.

Fast to deploy

Nothing to build. Nothing to maintain.

Upload or integrate your policies and control libraries, and they become live review templates in hours, not a six-month configuration project. HID Global onboarded 300+ products in under 3 months. Building a threat modeling tool in-house with AI means writing and maintaining the system indefinitely, with every new framework, regulation, or threat pattern costing another sprint. Clearly AI delivers expert-grade accuracy from day one and keeps pace with the threat landscape through exposure across all customers, so your engineers don't have to.

The real cost of a homegrown solution

Review coverage chart: over four weeks with Clearly AI, review coverage climbs to 100%, while a dashed line without it levels off at 10% coverage.

Enterprise-ready

Built by security engineers. Held to the same bar.

Founded by security engineers who ran hundreds of critical reviews at Amazon, Clearly AI is SOC 2 Type II audited and never trains models on customer data. Choose multi-tenant SaaS, a dedicated single-tenant environment, or deployment in your own cloud.

Explore trust, security, and deployment

  • RSAC Innovation Sandbox Finalist 2026
  • AICPA SOC 2 Type II
  • Y Combinator
  • Amazon Bedrock Builders' Challenge winner 2025

What Clearly AI customers are saying

  • 90%

    Reduction in review turnaround time

  • 4x

    Review capacity with the same headcount.

  • From 10 to

    100%

    Product coverage

Ericsson
“As soon as we started using Clearly AI, we saw an immediate reduction in the amount of time that not only my team was spending on the reviews, but that the business owners were actually spending having to give us the answers for the assessments.”

Ashley Haynes

Senior Director of Privacy, Trust and AI Governance

See Ericsson’s story
Four Ericsson colleagues working together around a table in a bright office.

FAQ

Answers to your top questions

What is Clearly AI?

Clearly AI is a continuous threat modeling platform for security, privacy, and GRC teams. Its agents gather context from design docs, code, tickets, and connected tools, then run structured reviews: threat models, privacy impact assessments, vendor risk reviews, and AI governance evaluations, with findings cited to source and gaps flagged. Teams use it both to triage many systems against baseline controls and to go deep on complex ones.

Who uses Clearly AI?

Product security, privacy, and GRC teams at mid-size and large enterprises, including Rivian, HID Global, and Ericsson. Security engineers, compliance analysts, and risk owners work on the same platform under the same license.

What is continuous threat modeling?

Continuous threat modeling means every change that ships gets a threat model, not just the fraction a team can review by hand. Reviews trigger automatically from Jira, GitHub, and other tools when work is created. Clearly AI gathers context from existing tickets, design docs, repos, and configs, then produces a structured threat model with findings, cited sources, and flagged gaps for engineers to review and sign.

Explore the platform

Is continuous threat modeling the same as continuous monitoring?

No. Monitoring tools watch running systems for issues after deployment. Continuous threat modeling assesses design and code changes as they're created, so risks are found before they ship. Clearly AI runs a structured review each time something new needs evaluation, triggered from the tools where work already starts.

How is Clearly AI different from traditional threat modeling tools?

Traditional tools require manual architecture diagramming and configuration before they produce anything. Clearly AI starts from the artifacts you already have. It also goes beyond threat models: privacy, vendor risk, AI risk, and compliance reviews all run on the same platform and audit trail.

See how Clearly AI compares

Which frameworks does Clearly AI support?

Clearly AI runs threat models against established methodologies such as STRIDE, OWASP, ATT&CK, and MAESTRO, along with custom frameworks built from your own policies and control libraries. The same engine runs privacy and compliance assessments against frameworks such as the EU Cyber Resilience Act and NY DFS Part 500.

Can we build this ourselves with an LLM?

You can, but you'd be writing and maintaining it indefinitely, and every new framework, regulation, or new threat vector would require another engineering sprint. Clearly AI delivers practitioner-grade accuracy from day one and improves from broad exposure to the threat landscape.

Build vs. buy: the real cost

How do we know the findings are accurate?

Every finding cites the document, ticket, or code that supports it, and answers are grounded in your own policies and standards. Reviewers can edit answers, add feedback, and regenerate individual answers. Every review runs against a specific version of the project and the template, so results stay consistent and auditable, and template changes can be tested against real projects before they go live.

Does Clearly AI work with our existing tools?

Yes. Clearly AI connects to issue trackers (Jira, ServiceNow, Linear, Azure DevOps, Aha!), code repositories (GitHub, GitLab, Azure Repos, Bitbucket), document sources (Confluence, Google Drive, SharePoint, Notion), and governance and security tools such as OneTrust, Archer, Snyk, and Wiz. Reviews trigger automatically from Jira, GitHub, ServiceNow, Linear, and Azure DevOps, and results route back as tickets, comments, and Slack messages. MCP-compatible AI assistants and IDEs connect through Clearly AI's MCP server.

See all integrations

Is Clearly AI a monitoring tool?

No. Clearly AI is an on-demand assessment platform. Each review is a point-in-time assessment of a specific project version, run when something new ships or changes. Reviews can be triggered from your existing workflow or run on a schedule; Clearly AI doesn't passively watch systems or dashboards.

How long does it take to get started?

A typical rollout connects your identity provider and source systems, loads your policies and standards, configures review templates to match your process, and tests a representative review against real sources. Most Clearly AI customers are up and running within days, and typically a pilot period shortcuts that further if you choose to do so. How long it takes depends on what you choose to review. HID Global, as an example, onboarded 300+ products in under 3 months.

Getting started guide

How is our data protected?

Clearly AI doesn't use customer data to train or fine-tune models; reviews work from your sources through retrieval, not training. The platform is hosted on AWS, with multi-tenant, single-tenant, and private cloud deployment options, encryption in transit and at rest, and SAML SSO and SCIM. Enterprises can bring their own model provider keys, including Amazon Bedrock, and choose alternative data residency. The SOC 2 Type II report is available under NDA.

Security documentation

Threat model everything that ships

The continuous threat modeling platform for product security, privacy, and GRC teams.

Cookies, in moderation

Essential cookies keep the site working. With your OK, analytics cookies (shared with our analytics providers) help us improve it. We never sell your data. See our Privacy Policy.