
Security Teams
Accelerate threat modeling, design reviews, and vendor risk assessments. Surface issues early and keep engineering moving.
Learn more
Clearly AI is the continuous threat modeling platform that automates the security review work that outpaces what your team can cover manually, so you can stop firefighting and actually get ahead of what ships.
Trusted by the companies you trust the most
Every review is manual. Pull people into a meeting, draw the architecture, consider the threat categories, then write it up. The recon alone takes days per review, before knowing if a single finding is real. So the backlog grows, and developers complain about the wait. AI-generated code is only widening the gap.
A continuous threat modeling platform, from intake to sign-off
Clearly AI gathers the context, drafts the assessment, and routes findings to where work happens. You focus your time on where human Judgment is needed.
Determine whether an employee question, new code change, or new feature ticket needs security’s eyes. Give employees answers quickly and auto-resolve low-risk changes.
Employees get answers grounded in policy
Goal: Fewer tickets, answer questions as they arise
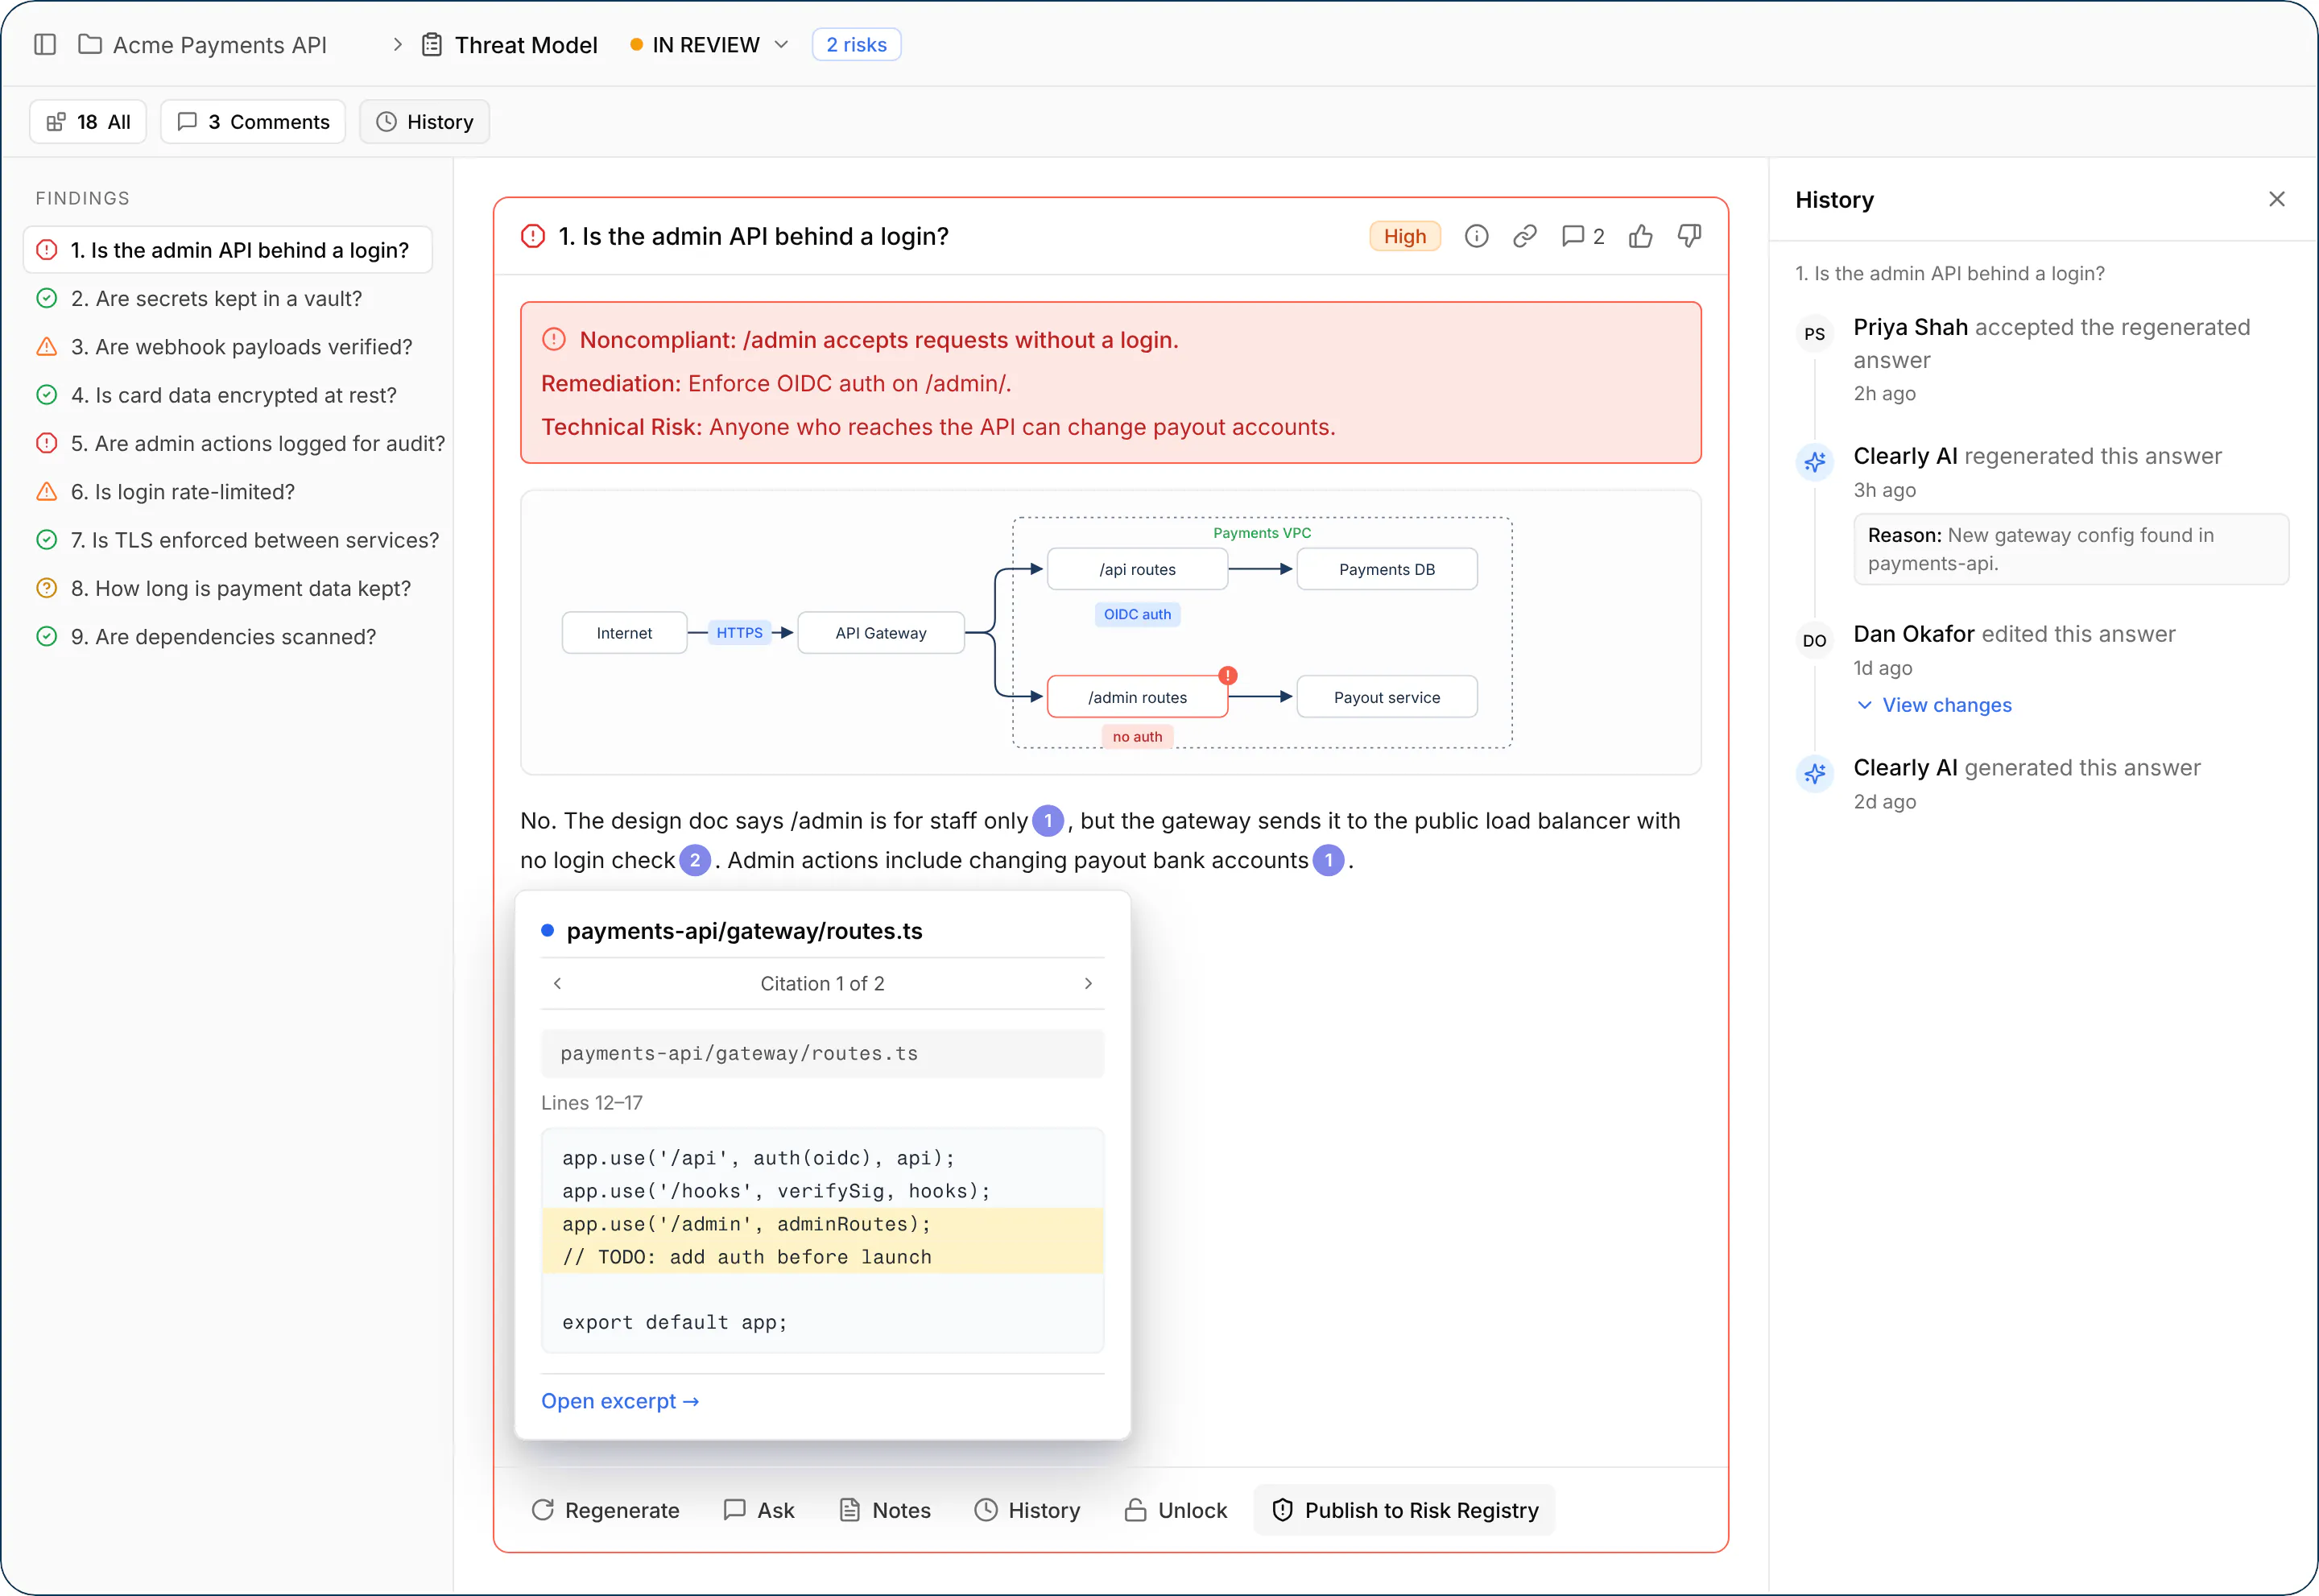
Generic AI gives you answers. Clearly AI gives you findings you feel confident about at scale. Each one links to the document, ticket, or code that supports it, so you can challenge it, get more detail, and sign off. Versioned templates make results consistent and auditable against a specific project state. Gaps get flagged and guesses aren’t tolerated.
Security teams do more than just threat modeling. They review vendors, assess data flows, evaluate AI systems, and map controls against compliance frameworks. Most tools cover one of those things well and leave the rest to a separate process, a separate configuration, and a separate license.
Clearly AI covers the full scope: threat models, privacy impact assessments, vendor risk assessments, AI risk reviews, and compliance control evaluations, all in one platform running against your policies and frameworks.
When you use Clearly AI for threat modeling, your privacy team and GRC function benefit, too. One investment extends across functions that were previously siloed.
Accelerate threat modeling, design reviews, and vendor risk assessments. Surface issues early and keep engineering moving.
Learn moreGenerate regulator-ready PIAs, DPIAs, and AI governance documentation in minutes. No more chasing teams for inputs.
Learn moreMaintain real-time visibility and produce structured audit-ready documentation across your security and privacy programs.
Learn moreIntegrations
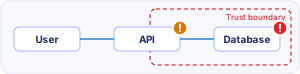
Reviews trigger automatically from Jira, GitHub, ServiceNow, Azure DevOps, and Linear. Context comes from design docs, code, tickets, wikis, and vendor documentation. Findings route back to Jira and Slack, where security and the business already work.
A new ticket, pull request, or record starts a review
Your team gets the results where they already work
Jira ticket, docs, diagrams, repos, Confluence, SharePoint, Wiz policies, baselines, URLs
Generates threat model, attack paths, mitigationsHighlights missing info & open questions
Security Champion or threat analyst validates, edits, and approves
Outcomes
90%
Reduction in review turnaround time
4x
Review capacity with the same headcount.
From 10 to
100%
Product coverage
“I would describe Clearly AI as the brain behind operations for privacy and security teams.”
Alec Deichman
Technical Privacy and AI Governance Manager
Road-tested enterprise expertise
Clearly AI has the domain depth of a security expert, not generic AI retrained for security. When it evaluates a threat model or a vendor questionnaire, it applies the same judgment a senior security engineer would: what's actually a finding versus noise, what context is missing, and what the next step should be. That judgment comes from the people who built it. Clearly AI was founded by security engineers who ran hundreds of critical reviews at Amazon, and the team includes senior and principal engineers from Amazon, Apple, and Microsoft.
FAQ
Continuous threat modeling means every change that ships gets a threat model, not just the fraction a team can review by hand. Reviews trigger automatically from Jira, GitHub, and other tools when work is created. Clearly AI gathers context from existing tickets, design docs, repos, and configs, then produces a structured threat model with findings, cited sources, and flagged gaps for engineers to review and sign.
No. Monitoring tools watch running systems for issues after deployment. Continuous threat modeling assesses design and code changes as they're created, so risks are found before they ship. Clearly AI runs a structured review each time something new needs evaluation, triggered from the tools where work already starts.
Traditional tools start with a blank canvas and require manual diagramming and configuration before producing findings. Clearly AI builds the model from artifacts your team already has. It also runs privacy, vendor risk, AI risk, and compliance reviews on the same platform.
Clearly AI supports STRIDE, MITRE ATT&CK, and MAESTRO for threat modeling and is deeply engrained in the market to track up and coming approaches. It also runs reviews against your own custom policies, control sets, and compliance frameworks. Upload a control spreadsheet and it becomes a live review questionnaire in real time.
Every finding links to the document, ticket, or code that supports it. Templates are versioned, so results are consistent and auditable against a specific project state. Your reviewers can challenge any finding before signing.
You can, but you'd be maintaining it indefinitely, and every new framework, regulation, or threat pattern means another engineering sprint. Clearly AI delivers practitioner-grade accuracy from day one and improves from exposure across all customers.
Bring a real ticket or doc to the demo. We'll run it live.